 1-800-284-5074


The relationship between a community bank or credit union and its members is built entirely on trust. When individuals deposit their savings or entrust you with their commercial accounts, they are betting that your institution is an impregnable fortress.
Historically, building that fortress was simple: thick concrete vaults, armed guards, and heavy steel bulletproof glass at the teller counter. Today, the battlefield has fundamentally shifted.
Modern banking infrastructure is a hybrid ecosystem. It stretches from physical branch lobbies and drive-thru NCR ATMs to cloud-hosted databases, edge-compute surveillance cameras, and customer-facing mobile applications. A vulnerability in any single node of this complex web can compromise the entire institution.
Implementing security procedures is no longer just a checkbox task for compliance examiners. It is an ongoing, real-life operation to defend your capital, reputation, and community.
This guide outlines the critical security procedures, fraud prevention strategies, and physical infrastructure protections required to shield your institution in a hyper-connected world.
1. The Dynamic Regulatory Framework: Designing Audit-Ready Protocols
Implementing security procedures without an underlying compliance framework is like building a house without a blueprint. For community financial institutions, your structural baseline is anchored by the Federal Financial Institutions Examination Council (FFIEC) and specific agency mandates like FDIC Part 326 or NCUA Part 748.
The FFIEC Architecture, Infrastructure, and Operations (AIO) Standard
The FFIEC AIO booklet shifted the regulatory focus from basic reactive IT audits to comprehensive operational resilience. Security procedures must reflect this shift by treating physical assets, digital networks, and third-party vendors as an interconnected ecosystem.
Asset Classification: You cannot protect what you do not know you own. Your procedures must mandate a dynamic asset registry that logs every endpoint—from a corporate laptop to a branch IP surveillance camera—along with its current patch status and risk tier.
Third-Party Oversight: If you outsource your infrastructure to a managed service provider, your security procedures must include continuous monitoring of their controls. This involves collecting annual SOC 2 Type II reports, testing their incident response times, and establishing clear liability boundaries within your Service Level Agreements (SLAs).
FDIC Part 326: The Physical Blueprint
FDIC Part 326 (Minimum Security Procedures) requires every insured bank to designate a dedicated security officer and implement a formal, board-approved security program. Your procedures must explicitly document:
The exact timelines and protocols for opening and closing branch facilities under dual-control parameters.
The maintenance schedules for all automated alarm systems, vault protections, and camera arrays.
The deployment of physical deterrents, such as high-visibility signage, impact-resistant glass, and tamper-evident locks on all cash enclosures.
2. Fortifying the Physical Edge: Intelligent Access Control and Monitoring
Physical branch locations and off-site ATMs remain the primary physical targets for coordinated criminal syndicates. Protecting this physical perimeter requires moving away from static deterrents toward intelligent, automated access control systems.
Eliminating the Single Point of Failure: Smart Credentials
Legacy brass keys and unencrypted proximity cards represent a catastrophic security risk. If a physical master key is duplicated or a generic badge is stolen, an intruder gains unrestricted access to your facilities.
Modern security procedures require identity-centric access control:
Encrypted RFID and Biometrics: Access to sensitive zones—such as server rooms, cash vaults, and core IT closets—must require encrypted smart cards combined with a secondary biometric factor (like a fingerprint or facial scan).
Role-Based Access Control (RBAC): Permissions must be restricted automatically based on the employee's role and working hours. A mortgage officer should not have access privileges to the teller cash drawers or the vault room at 10:00 PM on a Sunday.
Time-Bound One-Time Combinations (OTC): When external third-party vendors arrive to service an NCR ATM or repair an HVAC system, static lock combinations must be prohibited. Procedures must dictate the use of smart electronic locks that generate a unique, single-use code that expires automatically after a set window.
Verified Alarm Monitoring
A traditional alarm system simply calls a dispatcher when a circuit is broken, frequently resulting in false alarms caused by staff errors or environmental factors. Modern banking procedures require video-verified intrusion monitoring.
When a motion detector or seismic vault sensor triggers after hours, the alarm system must instantly stream the adjacent surveillance camera footage to a 24/7 central monitoring station. Trained operators verify the threat in real-time. If an active break-in is confirmed, they initiate a priority law enforcement dispatch, bypass false alarm penalties, and drastically reduce police response times.
3. Fraud Prevention at the Terminal: ATM Security in the Modern Age
ATMs are highly vulnerable endpoints. They sit in unmonitored public spaces, contain significant amounts of cash, and process thousands of card transactions daily. Criminals constantly innovate their tactics to target these machines through both physical and logical vectors.
Combating Physical Fraud: Advanced Skimming Prevention
Card skimming remains a multi-billion dollar threat to the banking industry. Fraudsters place sophisticated overlay devices over the native card reader slot to harvest magnetic stripe data while hidden pinhole cameras record customer PINs.
To mitigate this threat, your infrastructure procedures must include a layered defense:
Active Copious Anti-Skimming Devices: Install specialized hardware modules inside the NCR terminal that emit electromagnetic jamming fields. This disrupts the reading capability of any foreign magnetic head placed over the throat of the reader.
Tilt and Tamper Sensors: Integrate internal sensors that automatically trigger an alarm and take the ATM offline the moment the outer bezel or fascia experiences unusual physical force or displacement.
Transition to Contactless and EMV: Enforce strict processing rules that mandate EMV chip reading over legacy magnetic stripe fallback. Proactively encourage customers to use contactless mobile wallets (like Apple Pay or Google Pay) at the terminal, eliminating the physical insertion of cards entirely.
Preventing Logical Attacks: Defending Against Jackpotting
"Jackpotting" occurs when a criminal accesses the internal computer of an ATM (often by physically drilling into the plastic housing) and connects an external device loaded with malicious software. This software overrides the terminal's operating system, forcing the cash dispenser to eject all its currency.
Your logical infrastructure procedures must harden the ATM's internal PC:
Full Disk Encryption (FDE): Ensure that the ATM's hard drive is completely encrypted. If a criminal steals the drive or attempts to modify its contents offline, the data remains unreadable.
Whitelisting Software: Implement strict application whitelisting protocols. The ATM operating system must be locked down so that it blocks the execution of any piece of software or code not explicitly approved on an authorized list.
Physical Enclosure Security: Enclose the upper cabinet (top-hat) of the ATM with commercial-grade steel reinforcement brackets and pick-resistant locks, preventing quick, undetected physical access to the internal computer ports.
4. Video Surveillance as a Service (VSaaS) and Smart Optics
Video surveillance has transitioned from a passive forensic tool used to review crimes after they happen into an active, AI-driven preventative layer.
The Hybrid Cloud Storage Architecture
Relying on physical Digital Video Recorders (DVRs) stored in a back-closet creates a single point of failure. If an arsonist burns down a branch or a sophisticated robber steals the recording unit, your forensic evidence is permanently lost.
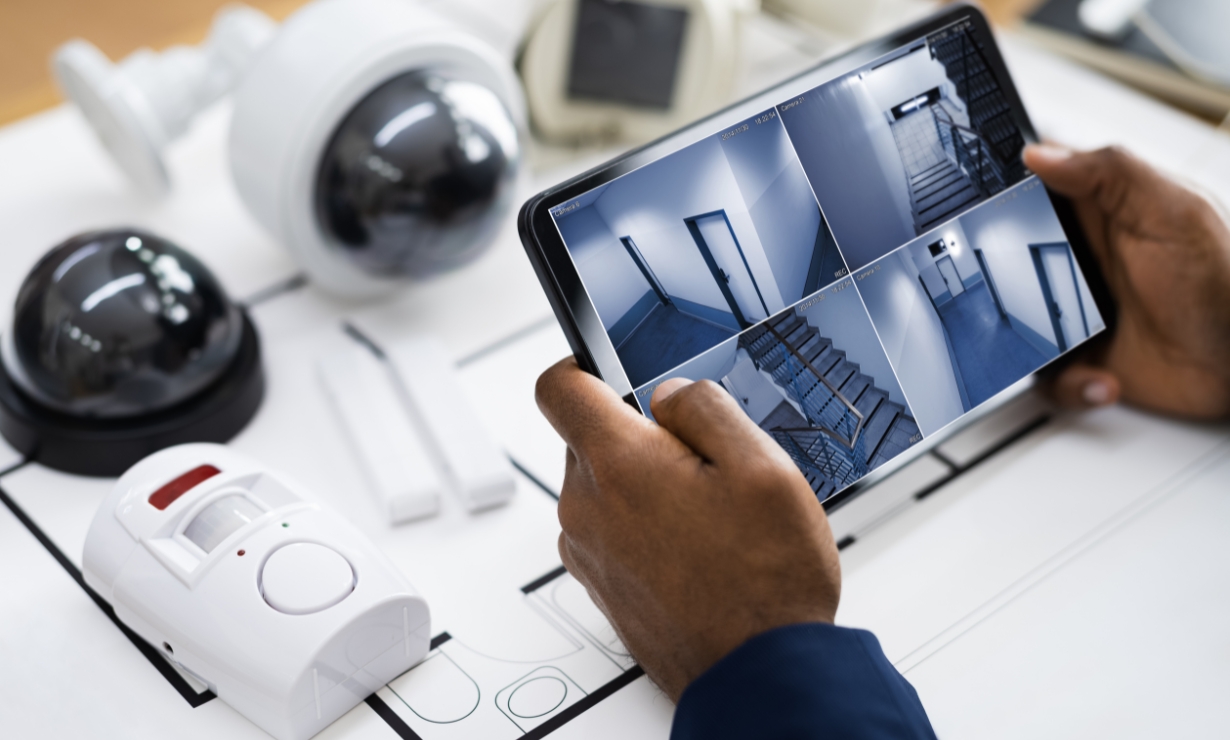
Implementing modern security procedures requires moving to a hybrid-cloud storage platform. Video is recorded continuously onto high-end IP cameras or a localized edge appliance for fast, low-bandwidth local playback. Concurrently, critical event clips—such as lobby entries after hours, alarm triggers, and ATM transaction windows—are automatically encrypted and streamed to a secure cloud repository. This ensures that your evidence remains pristine and accessible even if the physical branch is completely destroyed.
Leveraging Artificial Intelligence and Video Analytics
Modern IP cameras feature onboard processors capable of running complex machine-learning models. Your security infrastructure should utilize these analytics to flag suspicious behavior before a crime occurs:
Loitering Detection: If an individual lingers within a 5-meter radius of an outdoor ATM or night-deposit box for more than seven minutes between midnight and 5:00 AM, the camera flags the behavior and alerts remote monitoring staff.
License Plate Recognition (LPR): Deploy specialized high-speed cameras in your drive-thru lanes to automatically read and index license plates. If a vehicle associated with known check-fraud syndicates enters the lane, your security team receives an immediate dashboard notification.
Directional Line Crossing: Establish virtual fences within your software. If an individual crosses a designated line into an employee-only parking area or vault vestibule after hours, an alarm triggers instantly.
5. Humanizing Banking Infrastructure Security: Training and Cultivating a Security-First Culture
You can deploy millions of dollars in advanced encryption, biometric scanners, and AI-driven cameras, but your infrastructure is only as secure as the human beings operating it. Social engineering remains the most common method used by threat actors to bypass state-of-the-art security systems.
Defending Against Social Engineering and Tailgating
Criminals frequently exploit human empathy to bypass physical access controls. A common tactic involves a bad actor dressing up as a legitimate courier or utility repair technician, holding a heavy box, and waiting for an employee to politely hold the secure door open for them. This is known as tailgating or piggybacking.
Your procedures must institutionalize strict behavior protocols:
No Exceptions Badge Policies: Every single employee, executive, and visitor must scan their individual credential at every secure doorway, regardless of how well they are known to staff.
Interlocking Mantrap Portals: For high-security access points like main cash vaults or data hubs, utilize a dual-door mantrap system. The second door cannot open until the first door closes completely and the user clears authentication, physically limiting entry to one verified individual at a time.
Vetted Vendor Management: Establish a strict policy requiring all external service personnel to be scheduled in advance. If a technician arrives unannounced to service an NCR ATM, branch staff must keep the secure area locked until they verify the technician's credentials and work-order number with your managed service provider's central desk.
Continuous Security Awareness Education
Static, once-a-year training videos do not change human behavior. Building a security-first culture requires interactive, continuous training initiatives.
Phishing and Vishing Simulations: Regularly launch controlled, unannounced phishing emails and phone calls to test employee vigilance against social engineering. Use the results to provide immediate coaching to employees who fall for the simulation.
Robbery Readiness Drills: Conduct live physical security simulations with branch staff. Ensure every team member understands their exact role—such as how to safely activate silent panic buttons, how to observe suspect descriptions accurately, and how to preserve a crime scene for law enforcement.
The Ultimate Payoff: Turning Security into a Strategic Advantage
When a community financial institution implements cohesive, layered security procedures, the benefits extend far beyond a successful regulatory audit.
By consolidating your infrastructure protections—unifying your NCR ATMs, smart access controls, 24/7 video-verified alarms, and AI surveillance under a clear operational plan—you eliminate the friction that bogs down your internal teams. You replace unpredictable capital spikes with smooth operational workflows.
Most importantly, you create an environment where your customers and members feel completely secure. When people see that your drive-thru ATMs are brightly lit and free from tampering, that your staff is vigilant, and that your facilities utilize modern security technology, their trust in your brand deepens.
By securing your banking infrastructure today, you protect the financial backbone of your community tomorrow.